TL;DR

Play games on Amazon Luna for your game nights, included with Prime
- A rotating selection of games, no download needed
- Play on TV, laptop or phone
- Fast, free delivery for your gear, too
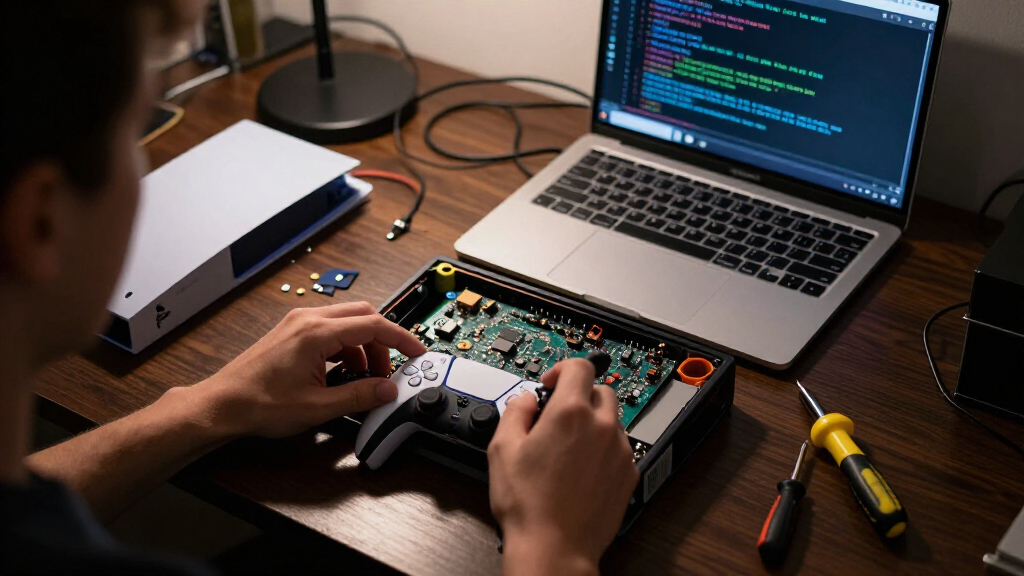
A developer group has published Relapse, a public exploit chain for the PlayStation 5 that works on firmware versions 7.00 through 13.60. The exploit uses a browser-based WebKit flaw combined with a kernel race condition to run custom ELF payloads, though Sony has not commented and patch status is unclear.
A newly published exploit chain called Relapse claims to enable unsigned code execution on PlayStation 5 consoles running firmware 7.00 through 13.60, a wide range that covers system software released across several years. The project, hosted on GitHub by developer ntfargo with a credited list of more than a dozen security researchers, chains a WebKit browser vulnerability with a kernel use-after-free race to gain read/write access to the console’s kernel and load custom ELF payloads.
According to the project’s GitHub repository, the exploit is triggered through the PS5’s web browser. Users are instructed to set the console’s Primary DNS to 45.56.67.85 or run a local Python server, then open the hosted exploit page on the console. The repository states that after a successful run, an ELF loader listens on port 9021, allowing custom payloads to be sent to the console.
The technical description outlines a two-stage attack. The browser stage uses JavaScriptCore info leaks and what the developers describe as “a structured clone object pool mismatch” to corrupt a typed array. The kernel stage then combines an address leak with a use-after-free race condition in aio_multi_wait, an asynchronous I/O kernel interface, to establish kernel read and write primitives.
The repository includes candid stability warnings: the WebKit stage “may need several attempts” and users should reload the page if the browser stalls, while the kernel exploit “may hang or panic the console,” requiring a reboot before retrying. The project carries a disclaimer stating it is intended “for educational and security research purposes only” and does not endorse piracy or unauthorized access. It also warns users they assume risks including system instability, data loss, and account bans.
Impact on PS5 Homebrew and Security
The broad firmware coverage — seven major firmware generations from 7.00 to 13.60 — makes Relapse one of the more widely applicable PS5 exploit chains made public. For security researchers and homebrew developers, the disclosed techniques, particularly the structured clone object pool mismatch and the aio_multi_wait use-after-free, provide documented examples of exploitable weaknesses in the PS5’s browser and kernel stack.
For Sony, the release increases pressure to patch both the WebKit flaw and the kernel race condition in a future system update. For ordinary users, the release raises the practical likelihood of unofficial software, and potentially piracy tools, spreading on consoles that remain on affected firmware — while also raising the risk that users attempting the exploit face crashes, data loss, or PlayStation Network account bans, risks the developers themselves acknowledge.
PS5 Hacking Efforts So Far
The PS5 has proven harder to compromise than its predecessor, and public end-to-end exploit chains have been rare. Much of the public research to date has come from established console security researchers, and the Relapse credits list includes several well-known names in the scene, among them TheFlow, who previously disclosed PlayStation vulnerabilities, and Sleirsgoevy, known for PlayStation 4 exploit ports.
The Relapse approach — entering through the console’s web browser — mirrors the strategy used widely against the PS4, where WebKit bugs served as the entry point for kernel exploits. By chaining a browser-stage memory corruption bug with a kernel-stage race condition, the project follows a familiar structure, but its firmware range extends to 13.60, covering relatively recent system software.
“This project is intended for educational and security research purposes only. It does not endorse piracy, unauthorized access, or misuse of commercial devices.”
— Relapse-Exploit GitHub repository
What Sony Hasn’t Addressed Yet
Sony has not publicly commented on the Relapse release, and it is not yet clear whether the underlying WebKit or kernel flaws are already fixed in firmware versions newer than 13.60, or how quickly a patch will arrive. Whether the exploit works reliably across all listed firmware versions, or only on some, is also not independently verified — the developers themselves note it can fail and crash the console.
It remains unclear how Sony will respond on the enforcement side. The project’s disclaimer warns of possible account bans, but Sony’s actual enforcement policy for users who run the exploit on their own consoles is unknown. Claims about the exploit’s capabilities rest on the developers’ own documentation and have not been independently confirmed by third-party security researchers in published analyses.
Expected Patch and Scene Response
The most likely near-term developments are a Sony firmware update addressing the WebKit and kernel vulnerabilities, which historically follows public disclosure of console exploits, and activity within the homebrew community to build payloads compatible with the port 9021 ELF loader. Users who want to preserve exploit access typically stay on vulnerable firmware, which creates a trade-off against security fixes and online features.
Independent security researchers may also publish analyses validating or contesting the exploit chain’s claims. Watch Sony’s official firmware release notes for the next system update, as patch notes would indicate whether the underlying bugs have been addressed.
Key Questions
Which PS5 firmware versions does the Relapse exploit support?
According to the project’s GitHub repository, Relapse supports firmware 7.00 through 13.60. It is not yet clear whether versions newer than 13.60 are also affected.
Is running the Relapse exploit risky?
Yes. The developers themselves warn that the kernel stage can hang or panic the console, and that users assume risks including system instability, data loss, and account bans. The software is provided as-is with no warranty.
Does Relapse enable piracy?
The project’s disclaimer states it is intended for educational and security research purposes only and does not endorse piracy or unauthorized access. However, an ELF loader capable of running custom code could in principle be used for other purposes, and the developers accept no liability for misuse.
How does the exploit work technically?
Per the documentation, the browser stage uses JavaScriptCore info leaks and a structured clone object pool mismatch to corrupt a typed array. The kernel stage then uses an address leak combined with an aio_multi_wait use-after-free race to gain kernel read/write access.
Will Sony patch this?
Sony has not commented, but console manufacturers routinely patch publicly disclosed vulnerabilities through firmware updates. Users on affected firmware should expect a fix in a future update, though timing is unknown.
Source: hn
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.